The Equifax Catastrophe: How One Missed Update Became a $700M Fine In most workplaces, ...
The Equifax Catastrophe: How One Missed Update Became a $700M Fine
In most workplaces, it’s common to delay non-urgent updates. A message comes in—on email, Teams, or chat—and gets pushed to “later.” Most of the time, nothing happens.
But in 2017, that “later” moment at Equifax turned into one of the largest data breaches in history.
What Equifax does
Equifax is one of the three major U.S. credit bureaus. It stores and analyzes highly sensitive financial data used for credit checks, loans, identity verification, and fraud prevention.
This makes it a critical part of the global financial system.
Tired of reminding staff to read your company policies?
DocRead makes compliance simple
What went wrong
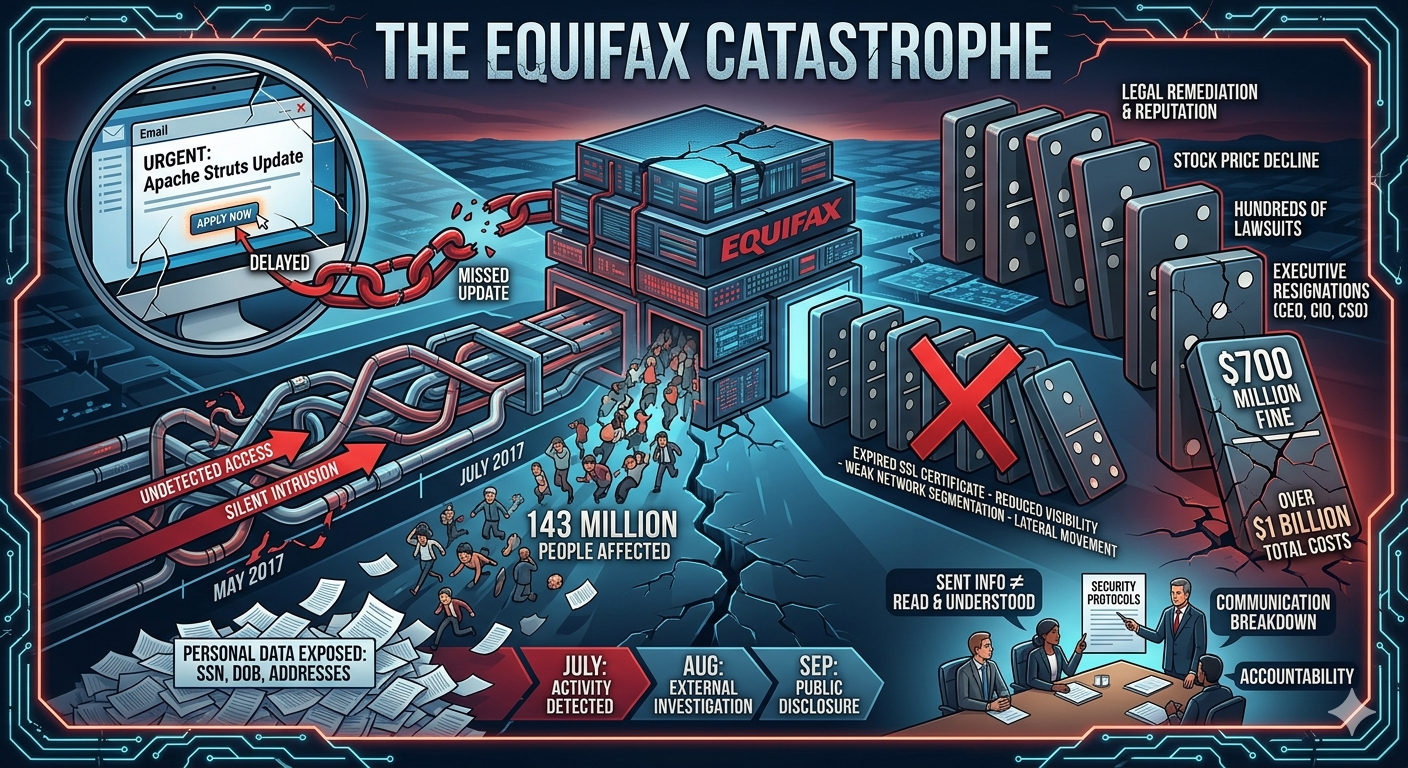
In May 2017, attackers exploited a known vulnerability in Apache Struts, a widely used web application framework.
A security patch had already been released—but it was never applied to a critical system.
That single missed update became the entry point.
How the breach unfolded
Once inside, attackers remained undetected for over two months.
Key events:
- May 2017: Initial breach through unpatched vulnerability
- July 2017: Suspicious activity detected; system taken offline
- August 2017: External cybersecurity firm brought in
- September 2017: Public disclosure released
By then, the damage was already done.
The critical detail most people miss
The attackers were not active only in July.
They had already gained access in May 2017 and remained inside Equifax systems for over two months—operating quietly, undetected, and extracting data slowly to avoid triggering alerts.
Root cause (and why it escalated)
This was not a sophisticated, unknown vulnerability.
It was a known issue with a known fix.
The patch for Apache Struts had already been released by the Apache Software Foundation. Equifax failed to apply it to a key system, leaving a publicly documented vulnerability exposed.
But the failure didn’t stop there.
Even after entry, multiple systemic weaknesses amplified the breach:
- A monitoring system failed due to an expired SSL certificate, limiting visibility into encrypted traffic
- Weak internal network segmentation allowed attackers to move laterally across systems
- Data was exfiltrated slowly over weeks, delaying detection
- Despite discovery in late July, public disclosure did not occur until September 7
This combination of missed patching, reduced visibility, and weak internal controls turned a preventable issue into a large-scale breach.
Are your policies read on time and by the right people?
DocRead makes compliance simple
What was exposed
The breach affected about 147 million people, exposing:
- Names
- Social Security numbers
- Birth dates
- Addresses
- Driver’s license numbers
Additional exposure included:
- Credit card data (~209,000 users)
- Dispute documents (~182,000 users)
- Data from UK and Canadian individuals
Why it became so severe
This was not a zero-day attack or unknown exploit. It was a known vulnerability with a known fix.
But multiple failures compounded the issue:
- A missed security patch left systems exposed
- An expired SSL certificate reduced monitoring visibility
- Weak network segmentation allowed lateral movement
- Slow data exfiltration delayed detection
- Public disclosure was delayed after discovery
The result: attackers operated inside Equifax systems undetected for weeks.
The impact
The consequences were significant:
- Up to $700 million settlement with regulators
- Over $1 billion in total costs (legal, remediation, reputation)
- Hundreds of lawsuits filed
- Significant stock price decline
- Executive resignations, including the CEO, CIO, and CSO
The core lesson
The Equifax breach is often framed as a cybersecurity incident. But at its core, it was much simpler:
A known patch existed.
It was not applied.
And “later” became a two-month silent intrusion into one of the world’s most sensitive data systems.
Taking accountability
The breach led to major executive departures. CEO Richard F. Smith stepped down shortly after the incident became public, followed by CIO David Webb and CSO Susan Mauldin.
These resignations reflected not just technical failure, but broader breakdowns in governance, risk management, and accountability.
The Equifax breach is often remembered as a cybersecurity incident.
But at its core, it was something simpler—and more common.
A known patch existed, a critical update was missed, and “later” became a two-month undetected intrusion inside one of the most sensitive data systems in the world.
How DocRead helps reduce this risk
The Equifax incident wasn’t only a technical failure—it was also a breakdown in communication, accountability, and follow-through.
DocRead helps address this gap in Microsoft 365 and SharePoint by ensuring critical updates, policies, and compliance documents are:
- Distributed properly
- Acknowledged by employees
- Tracked with audit visibility
Because sending information is not enough—organizations need proof it was read and understood.
Final thought
Most major breaches don’t start with sophisticated attacks. They start with small oversights: a missed update, an unverified assumption, or a delayed action.
Equifax is a reminder that in cybersecurity, “later” can become the most expensive decision an organization ever makes.
Get your free Standard Operating Procedures guide
Creating Standard Operating Procedures for your organisation doesn't have to be complicated. This guide will introduce you to the whole lifecycle from creation to training and distribution.
You may also like:
October 2, 2026
September 18, 2026
How to Manage Policy Exceptions in Microsoft 365 Without Losing Audit ControlPolicies are designed ...
September 11, 2026
Contractor Policy Acknowledgment: How to Track Compliance for Third PartiesOrganizations often rely on contractors, ...
August 28, 2026
How Do You Migrate Legacy Policies into a Policy Management System?For a lot of ...
August 28, 2026
What Features Should You Look for in Policy Management Software for SharePoint?Choosing policy management ...
July 10, 2026
How Long Does It Take to Implement Policy Management Software in Microsoft 365?When organizations ...