The Equifax Catastrophe: How One Missed Update Became a $700M Fine In most workplaces, ...
SOX Compliance with Collaboris and DocRead: Making Governance Practical
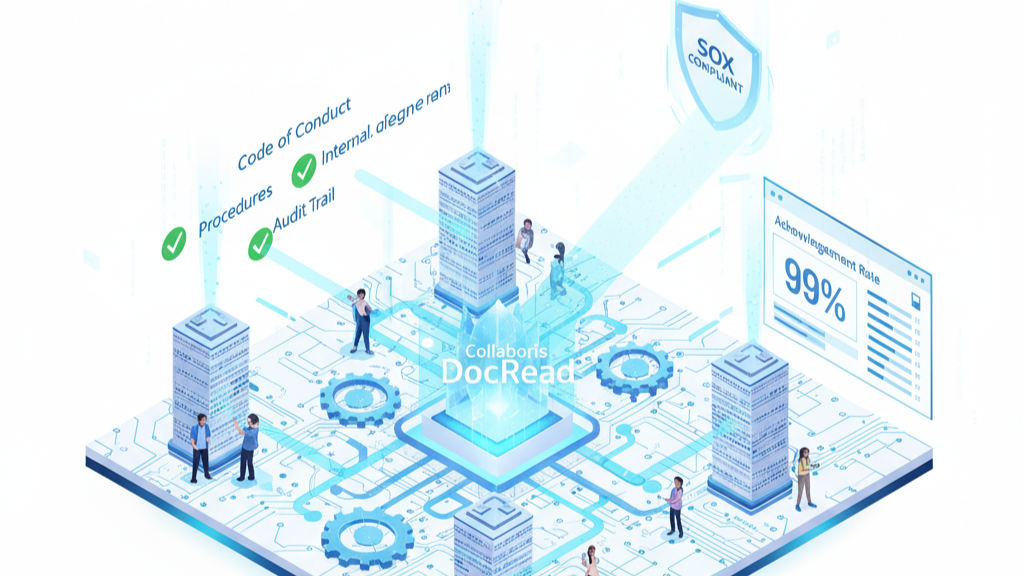
The Sarbanes-Oxley Act (SOX) remains one of the most critical frameworks for companies that want to maintain investor trust. It ensures that financial reporting is accurate, internal controls are sound, and corporate disclosures are reliable.
The challenge? SOX compliance isn’t just about finance teams — it touches HR, IT, and operations. And while many organizations focus on controls, they often overlook one key piece: ensuring people actually read, understand, and follow those controls.
This is exactly where Collaboris and DocRead bridge the gap.
1. Code of Conduct: Setting the Tone at the Top
Every SOX-compliant company must have a documented code of conduct and ethics policy. But having a code isn’t enough — regulators expect evidence that employees have reviewed and acknowledged it.
Example:
A publicly traded retailer used DocRead to distribute its updated ethics policy to more than 20,000 employees worldwide. Within 30 days, they achieved a 96% acknowledgment rate — complete with a digital paper trail for auditors.
Tired of reminding staff to read your company policies?
DocRead makes compliance simple
2. Internal Control Procedures: Distributing the Right Information
SOX Section 404 requires management to document and test internal controls over financial reporting. DocRead allows organizations to assign relevant procedures to specific roles, ensuring that only the right employees are asked to review them — reducing noise and improving compliance rates.
Example:
A global logistics company used DocRead to target specific internal control procedures to finance managers, system owners, and IT admins. This kept everyone aligned on their responsibilities and reduced instances of control failures caused by miscommunication.
3. Audit Trail and Accountability
When auditors ask for proof that employees were informed of financial control changes, DocRead delivers. Its reporting capabilities make it easy to demonstrate not just that controls exist, but that they were communicated, read, and acknowledged by the right people.
Example:
A tech company undergoing its first SOX audit was able to present clean, timestamped acknowledgment reports for every control procedure — reducing audit time and earning commendation for their documentation maturity.
Are your policies read on time and by the right people?
DocRead makes compliance simple
Bottom Line:
SOX compliance is about more than financial statements — it’s about culture, governance, and accountability. Collaboris and DocRead make compliance a proactive, well-documented process rather than a last-minute scramble.
Get your free Standard Operating Procedures guide
Creating Standard Operating Procedures for your organisation doesn't have to be complicated. This guide will introduce you to the whole lifecycle from creation to training and distribution.
You may also like:
October 2, 2026
September 18, 2026
How to Manage Policy Exceptions in Microsoft 365 Without Losing Audit ControlPolicies are designed ...
September 11, 2026
Contractor Policy Acknowledgment: How to Track Compliance for Third PartiesOrganizations often rely on contractors, ...
August 28, 2026
How Do You Migrate Legacy Policies into a Policy Management System?For a lot of ...
August 28, 2026
What Features Should You Look for in Policy Management Software for SharePoint?Choosing policy management ...
July 10, 2026
How Long Does It Take to Implement Policy Management Software in Microsoft 365?When organizations ...