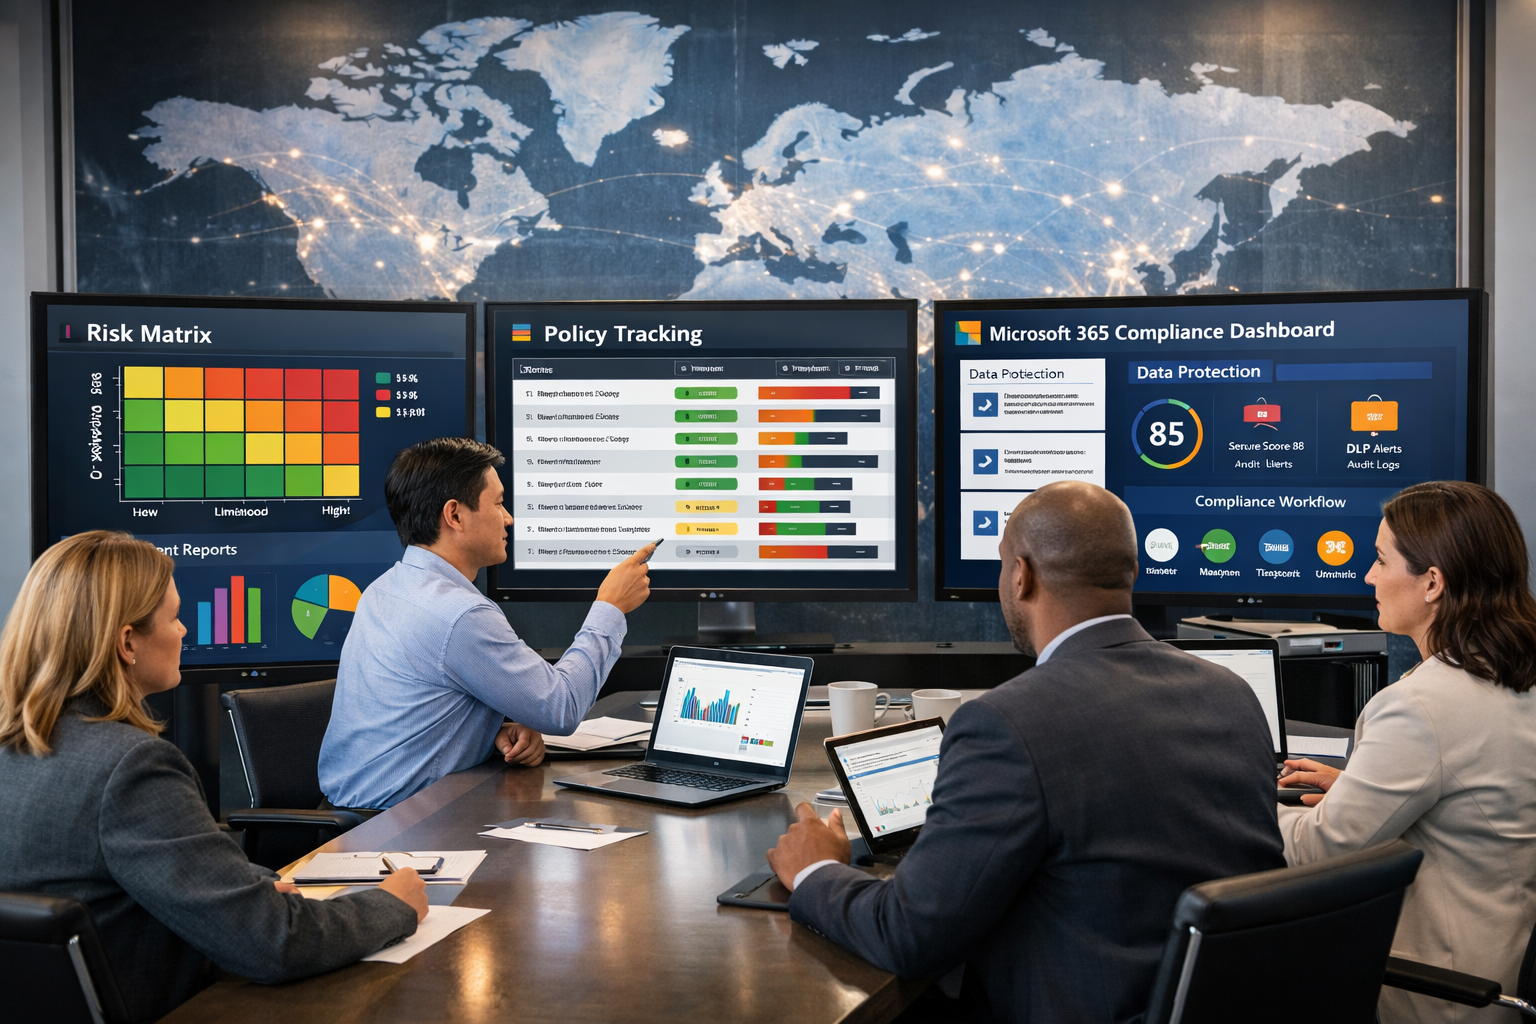
Compliance Risk Management Framework: How to Assess, Prioritize, and Control Regulatory Risk
Most compliance failures don’t start with a missing policy. They start when a policy exists but nobody checks that it reached the right people, that they read it, or that the control behind it actually ran. Equifax is the familiar example. According to the FTC, the company was alerted to a critical software vulnerability in […]
Read more